 Kaldera
You choose the master password
Argon2id stretches it into a key. The parameters are recorded in the vault, so an existing vault never silently gets weaker or stronger.
Product / Password vault
Five record types, folders, tags, smart folders and full-text search — all encrypted on your device, all readable offline.
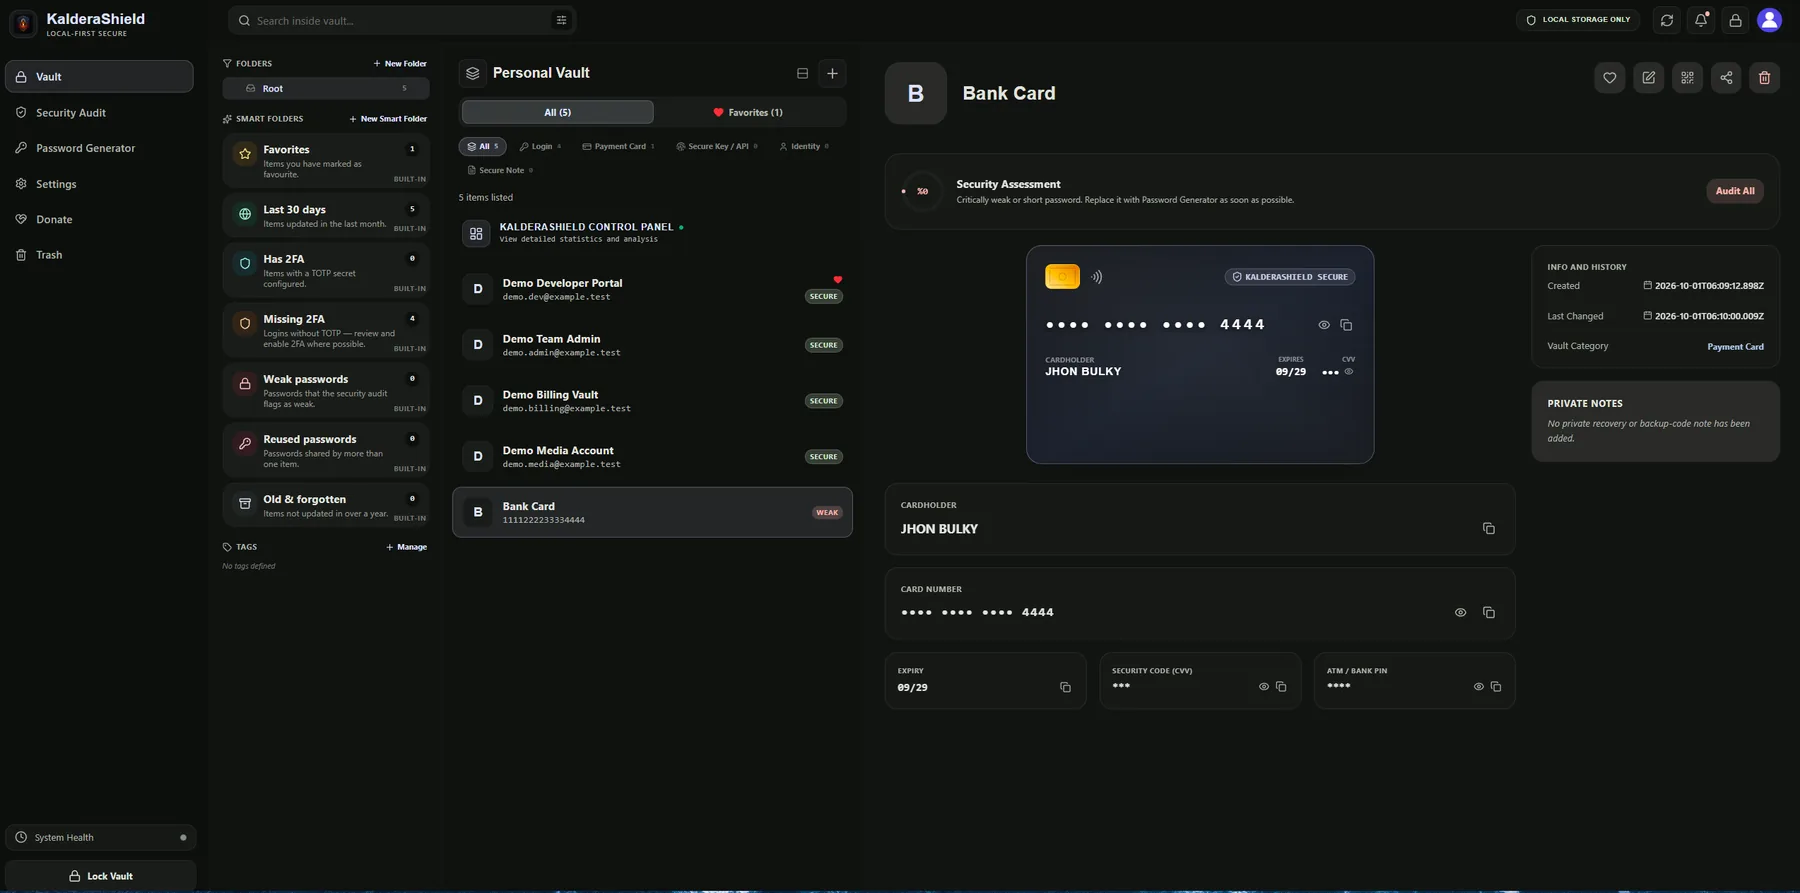
The vault stores five kinds of record: logins, payment cards, identities, secure keys and secure notes. Every record is encrypted with its own key, so one record being broken never reveals another.
Organisation is local too. Folders, tags, favourites and built-in smart folders such as "has 2FA" or "missing 2FA" are computed on the device from your own data, not from a server-side index.
Search runs locally across titles, usernames and URLs, with diacritic-insensitive matching, so it keeps working with no connection at all.
Argon2id stretches it into a key. The parameters are recorded in the vault, so an existing vault never silently gets weaker or stronger.
A unique 256-bit AES-256-GCM key is derived per record through WebCrypto HKDF-SHA256, using the record id as the salt.
Titles, usernames, passwords and notes are masked in the SQLite columns; the real values exist only inside the encrypted payload.
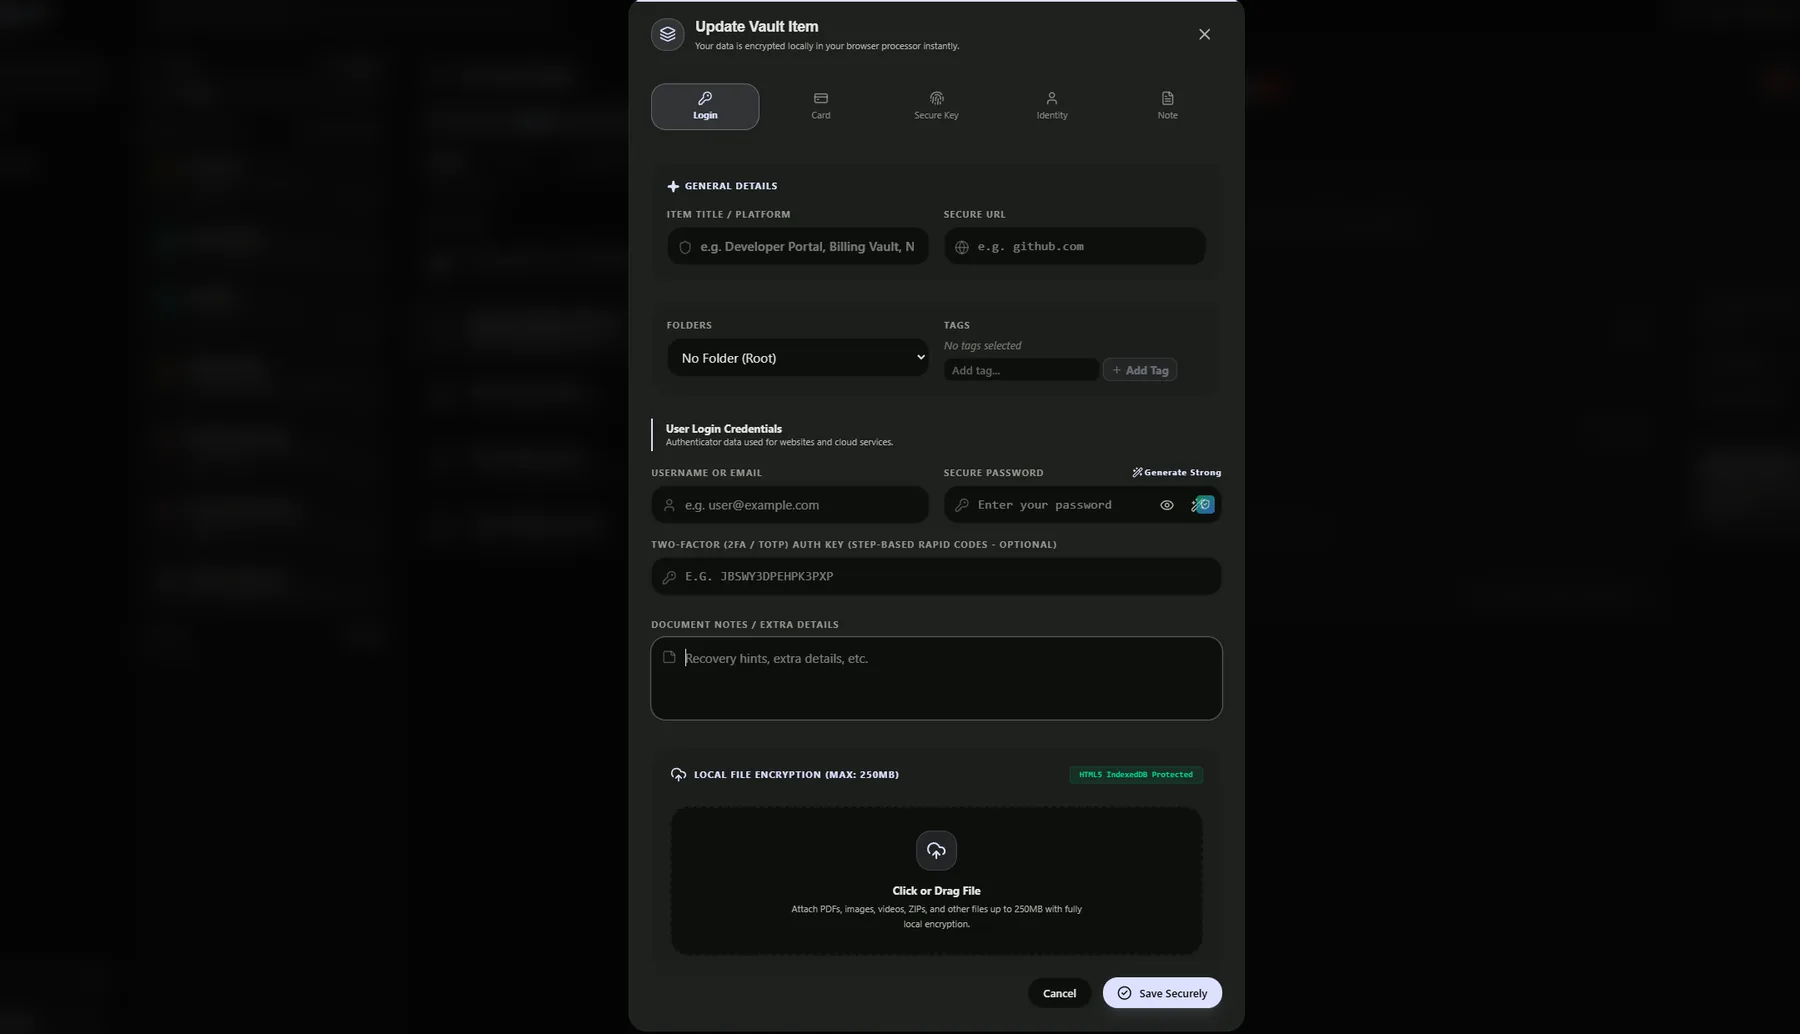
Logins, cards, secure keys, identities and notes share one editor, and a payment card keeps its number, expiry, CVV and ATM PIN in separate masked fields.
Every record is encrypted on your device with a key that never leaves it. Protection still depends on your master password strength, the KDF parameters stored in your vault, the security of the device itself, and how you use the application. No cryptographic design promises absolute protection against every attack, and a compromised device can read a vault that has already been unlocked.
New desktop and Android vaults use 64 MiB of memory, 4 iterations and 2 lanes. Web builds use 32 MiB, 3 iterations and 1 lane.
Breaking one record does not reveal any other record in the vault, because no two records share a key.
Sensitive columns hold a static placeholder token. The plaintext exists only inside the AES-256-GCM payload.
You can unlock with the 24-word BIP-39 recovery key and reset the password, or restore an encrypted backup. Without either, the vault cannot be opened, because nothing on your device can re-derive the key.
Yes. Export an encrypted backup and restore it on the other device with your master password. The vault file is portable and not tied to one machine.
No. Search runs against the local database on your device, including diacritic-insensitive matching.